


News

Ransomware report: 78% of Australian victims pay up as businesses abandon negotiations
New research reveals Australian businesses are increasingly paying ransomware demands, with four in 10 victims handing ...

Aussie government flags 18 recommendations from its AI Rapid Review
Australian laws may soon change to criminalise instances of rogue AI behaviour and legislate mandatory reporting in the ...
Op-Ed: Microsoft November Patch Tuesday reveals 1,092 vulnerabilities
Microsoft’s Patch Tuesday features more than a thousand Windows vulnerabilities.
Qantas HQ to outsource 850 jobs to Accenture as airline’s investments in AI ‘step up’
Qantas has informed staff that it intends to remove 850 local jobs from its Mascot HQ through a partnership with ...

Australia to force frontier AI firms to meet mandatory safety standards
The Albanese government plans to legislate mandatory AI safety obligations, backed by a dedicated regulator with powers ...
You’re an *SSHole: Exploitation of OpenSSH vulnerability is speeding up
Security researchers are observing activity increasingly targeting CVE-2026-123158 less than a week after its disclosure ...

White House nominates Palantir CISO Michael LoSapio to direct CISA
The top US cyber agency has been without a director for almost two years after the previous boss resigned on Donald ...
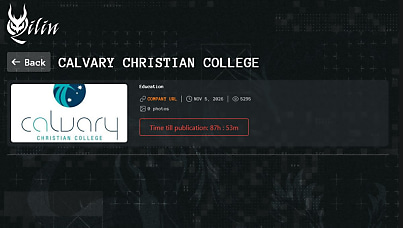
Exclusive: Townsville’s Calvary Christian College investigating cyber incident
The school says the system holding permission forms was affected by the attack, as the Qilin ransomware group threatens ...

The big melt: France pins supermarket fridge cyber attacks on Iran
French government vows revenge as foreign minister calls the attack “unprecedented in both its scale and its level of ...
Explainer: What’s driving the rapid rise in new ransomware groups?
The number of organisations listed on darknet leak sites has risen, with new groups driving more than 90 per cent of ...
SonicWall discloses pair of vulnerabilities in end-of-life Global Management System
The network appliance maker says it will do nothing to address CVE-2026-109593 and CVE-2026-109594; customers are urged ...
Patch now! Zyxel patches switches left vulnerable since June
The networking firm thought it had shut the gate on one vulnerability, only to have hackers target another and ...
Report: Australian businesses want more than technical support from MSPs
With 68 per cent of Australian organisations already using managed service providers and another 28 per cent considering ...
Aussie recycled toilet paper brand Who Gives a Crap discloses data breach
The company’s chief executive says Australian, US, and UK customers were affected after a third-party incident at a US ...
AI stocks tumble in wake of midterms rout, impact on Aussie companies uncertain
Fears of an AI crackdown have driven a trillion-dollar crash in technology stocks after a Democrat “blue wave” in the ...
Gone in 35 minutes: Hackers are turning public research into active exploits faster than ever
New research reveals that more than 90 per cent of vulnerabilities with public proof-of-concept code are taking just ...

Digital Transformation Agency’s new AI Reference Architecture is ‘the right call’, says Kinetic IT CTO
The DTA’s new guidance offers government agencies a “shared foundation for designing and governing AI systems”.
DigiCert discloses ‘security event’, says customer data exposed
The company has warned some customers that their personal information has been compromised, with passports and driver’s ...

Update now! Newly disclosed OpenSSH password flaw could lead to brute-force hacking, expert warns
A 10-year-old flaw in OpenSSH could allow an attacker to use any password between 257 and 1,024 characters to access ...
Westpac ditches Palantir following activist push
Major bank Westpac has announced that it will end its partnership with US surveillance firm Palantir.