


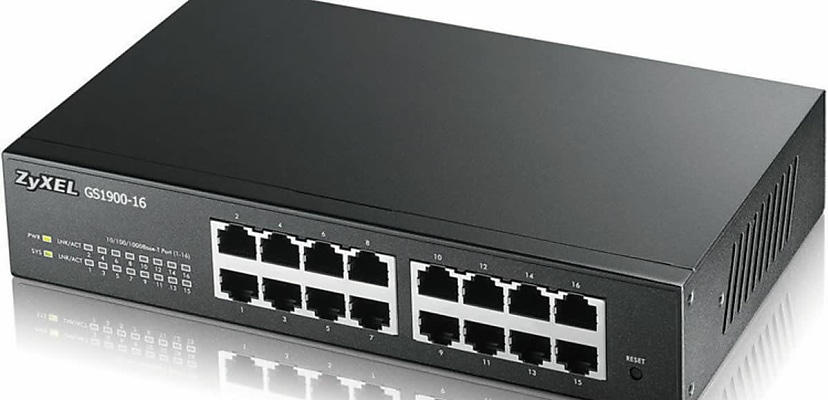
Throughout September, unidentified hackers targeted an unpatched zero-day in Zyxel GS1900 switches, leading to the compromise of nearly 1,000 devices that were thought to be secure.
Attackers exploited the only recently disclosed CVE-2026-107441 to execute unauthenticated remote commands, compromising approximately 996 devices across 48 countries.
Initially mistaken for CVE-2026-7273, the campaign enabled attackers to steal configurations and credentials and deploy malicious tools.
The newer vulnerability impacts firmware versions 2.90(AAHH.2)C0 and earlier. Zyxel has since released a security update, and the company is urging customers to update for “optimal protection”.
Jake Knott, head of threat intelligence at cyber secrurity firm watchTowr, breaks down the timeline and how hackers may be exploiting zero-days such as CVE-2026-107441.
“On November 3rd, Zyxel disclosed CVE-2026-107441, an unauthenticated out-of-bounds write vulnerability affecting Zyxel GS1900 switches. In September, a campaign that had compromised nearly 1000 GS1900 switches was observed and widely reported, and it was attributed to CVE-2026-7273 at the time,” Knott recapped for Cyber Daily.
“According to Binarly’s analysis, the exploit used in these intrusions worked against firmware already patched for CVE-2026-7273 by abusing a separate, previously unpatched zero-day in the same code, now tracked as CVE-2026-107441.
“Attackers will continue to use whatever works. The attacker behind this campaign, or one closely related, is believed to have exploited known vulnerabilities, pulled public exploit code from GitHub, reproduced n-day vulnerabilities, and, as seen here, has the capability to build, develop, and/or obtain zero-day exploits as well.”

However, Knott did admit he was none-the-wiser about how the zero-day was initially discovered.
“We don’t know how this particular exploit was built, identified, or obtained. Whether it came from an LLM, a fuzzer, or old-fashioned human intelligence, finding bugs has never been cheaper or faster,” Knott said.
“Every patch telegraphs exactly where attackers should look, and incomplete fixes or adjacent bugs are naturally the first things they'll look for next, as in this case.”
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.
