

Security
In conversation with ThreatLocker’s founder and CEO, Danny Jenkins
Danny Jenkins was recently in Sydney for one of the company’s Control+Alt+DELight events, and we caught up with him to ...

Australia’s peak cyber security body welcomes Essential Eight evolution
The ASD’s new Essentials framework is a step in the right direction, says the Australian Information Security ...

Exclusive: Poole Group investigating LockBit ransomware attack
An Aussie accounting firm is listed as a hacking victim; OAIC and the Australian Taxation Office have been informed of ...

The industry speaks – part 7: Cyber Security Awareness Month 2026
“The better question for every boardroom is simpler and harder: when, not if, we are breached, how much of our business ...

Exclusive: Hunter Neurology investigating patient data breach claims
The n0n ransomware group says it has tens of thousands of patient records as healthcare provider Hunter Neurology ...
Essential Eight evolved: Aussie cyber agency launches ASD Essentials
The Australian Signals Directorate has launched the first three chapters of its latest take on cyber security resilience

Patch now! GitLab publishes fixes for perfect-10 vulnerability CVE-2026-97229
Exploitation has not occurred yet, but owners of self-managed GitLab CE and EE instances need to act now – before it’s ...

Op-Ed: When a hospital can’t patch a machine, what’s the backup plan?
There is a reason why a hospital’s critical infrastructure is often at risk from hacking campaigns: vulnerabilities in ...

The industry speaks – part 6: Cyber Security Awareness Month 2026
“As organisations embrace AI to drive productivity and innovation, attackers will use the same technologies to scale ...
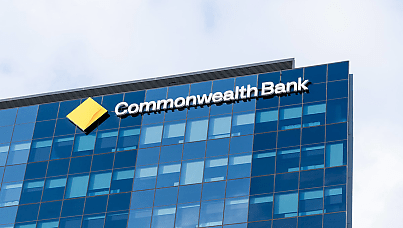
CBA denies offshoring following construction of Indian office complex
The Commonwealth Bank of Australia is under fire after it constructed a new office complex in India; the bank claims the ...
The big melt: How Australia can stop a French-style refrigerator hacking campaign
Wherever there are refrigeration controls connected to the internet, there is risk, says Claroty’s Jason Pearce.
Patch now! Hackers already targeting newly disclosed Ivanti Connect Secure zero-day
CVE-2026-104935 is a high-severity authentication bypass that one analyst calls “incredibly simple” to exploit, as CISA ...
Op-Ed: Microsoft October Patch Tuesday reveals 1,413 vulnerabilities
Microsoft is publishing 1,413 own-product vulnerabilities on October 2026 Patch Tuesday, including 1,102 vulnerabilities ...