


Australian holiday-makers are being warned to be on the lookout for suspicious messages after a global third-party booking system appears to have been compromised by a cyber security incident.
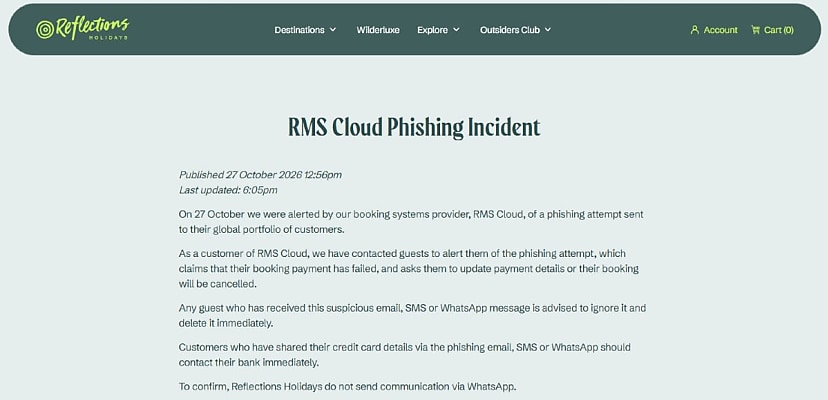
“We are contacting you as a past guest to make you aware our third-party booking system provider, RMS Cloud, has confirmed a global incident,” a spokesperson for the New South Wales-based Reflections Holidays said in an email seen by Cyber Daily.
“This involves phishing emails, SMS and WhatsApp messages that were sent to some Reflections Holidays guests, along with many other accommodation providers.
“The messages claim a booking payment has failed and asks the recipient to update their payment details or their reservation will be cancelled.”
The email, sent on October 27, confirmed that these were phishing attempts and not legitimate communications. The company had further advice on its website.
“Any guest who has received this suspicious email, SMS or WhatsApp message is advised to ignore it and delete it immediately,” Reflections Holidays said.
“Customers who have shared their credit card details via the phishing email, SMS or WhatsApp should contact their bank immediately.”
BIG4, G'day Parks, and several other Australian companies are understood to have also begun contacting customers, according to reporting by the ABC.

RMS Cloud – which is used by more than 6,000 holiday parks, hotels, and campgrounds around the world – began monitoring malicious activity in the last 24 hours.
“RMS is investigating reports of guests receiving phishing messages via WhatsApp, SMS and email that reference genuine booking information and ask recipients to confirm payment details or make a payment,” the company said on its status page.
“These messages are not being sent by RMS.
“Our teams are actively investigating the activity and taking steps to contain it, protect customer information and support affected customers and integration partners. Some integrations may experience brief interruptions while this work continues.”
RMS Cloud provided a “guest email template” for its customers on the same day, and began pursuing “the removal of contact channels and websites used in the scam”.
The next day, RMS Cloud began issuing new credentials to its integration partners, as well as providing assistance to complete the process.
“We are pursuing the removal of the websites and contact channels used in the scam,” the company said in an October 28 update.
“We know you want more detail about what happened and what it means for your property. We are preparing a fuller update and will share more throughout the day as it becomes available.
“RMS will never ask you or your guests for card details or payment through WhatsApp.”
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.
