


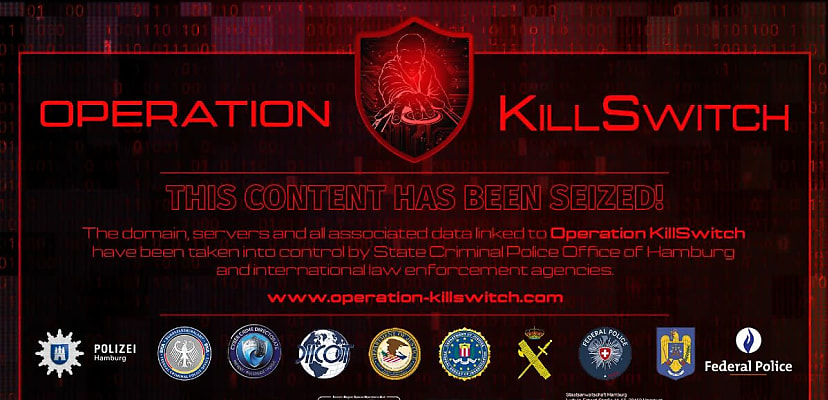
Operation KillSwitch, led by German authorities, has disrupted the KillSec ransomware group after investigators identified around 1,000 suspected attacks worldwide, including about 500 believed to have succeeded.
The 30 September operation secured at least 110 terabytes of stolen data from KillSec’s leak site, which the group used to threaten victims with publication unless they paid a ransom.
Authorities provisionally arrested three suspects and searched eight properties across Greece, Romania, Spain and the UK, while also targeting cryptocurrency and other criminal proceeds.
KillSec has operated since around 2024, exploiting software vulnerabilities and poorly secured access points, particularly cloud storage, to steal sensitive organisational data.
Investigators also found evidence that the group used AI to build and maintain its ransomware infrastructure and identify potential victims.
The investigation identified suspected roles including an administrator, developer, negotiator and affiliate. The alleged main operator and administrator is 16 years old, while a suspected developer turned 18 in August 2026 and was a minor when some alleged offences occurred.
Authorities brought five central servers under police control and seized KillSec-operated domains, redirecting visitors to law enforcement notices.
The operation involved authorities from Belgium, Finland, Germany, Greece, the Netherlands, Romania, Spain, Switzerland, the UK, and the US, alongside Europol and Eurojust.

Bitdefender and Group-IB also supported the investigation. Alexandru Nicola Stoica, Senior Threat Researcher on Bitdefender’s DracoTeam, said she was pleased with the operation’s outcome.
“This action exemplifies the power of collaboration between the public and private security sectors in dismantling criminal operations, in this case, a prolific ransomware group that caused significant harm to victims,” Stoica said in a statement.
“It also reinforces an important message to threat actors: no infrastructure is beyond the reach of a coordinated, international effort.”
Investigators are continuing to analyse seized devices and data, which could identify further victims, attacks, and individuals linked to the group.
KillSec has claimed several Australian victims in recent years, including creative agency Fancy Films, IT services provider Hexicor, and Wendy Wu Tours.
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.
